Widevine L1 for Hotel TV: What to Verify Before You Promise…
September 30, 2026
Research period: September 2026
By COTT.TV Hospitality Technology Research Desk·Published September 30, 2026·5 min read

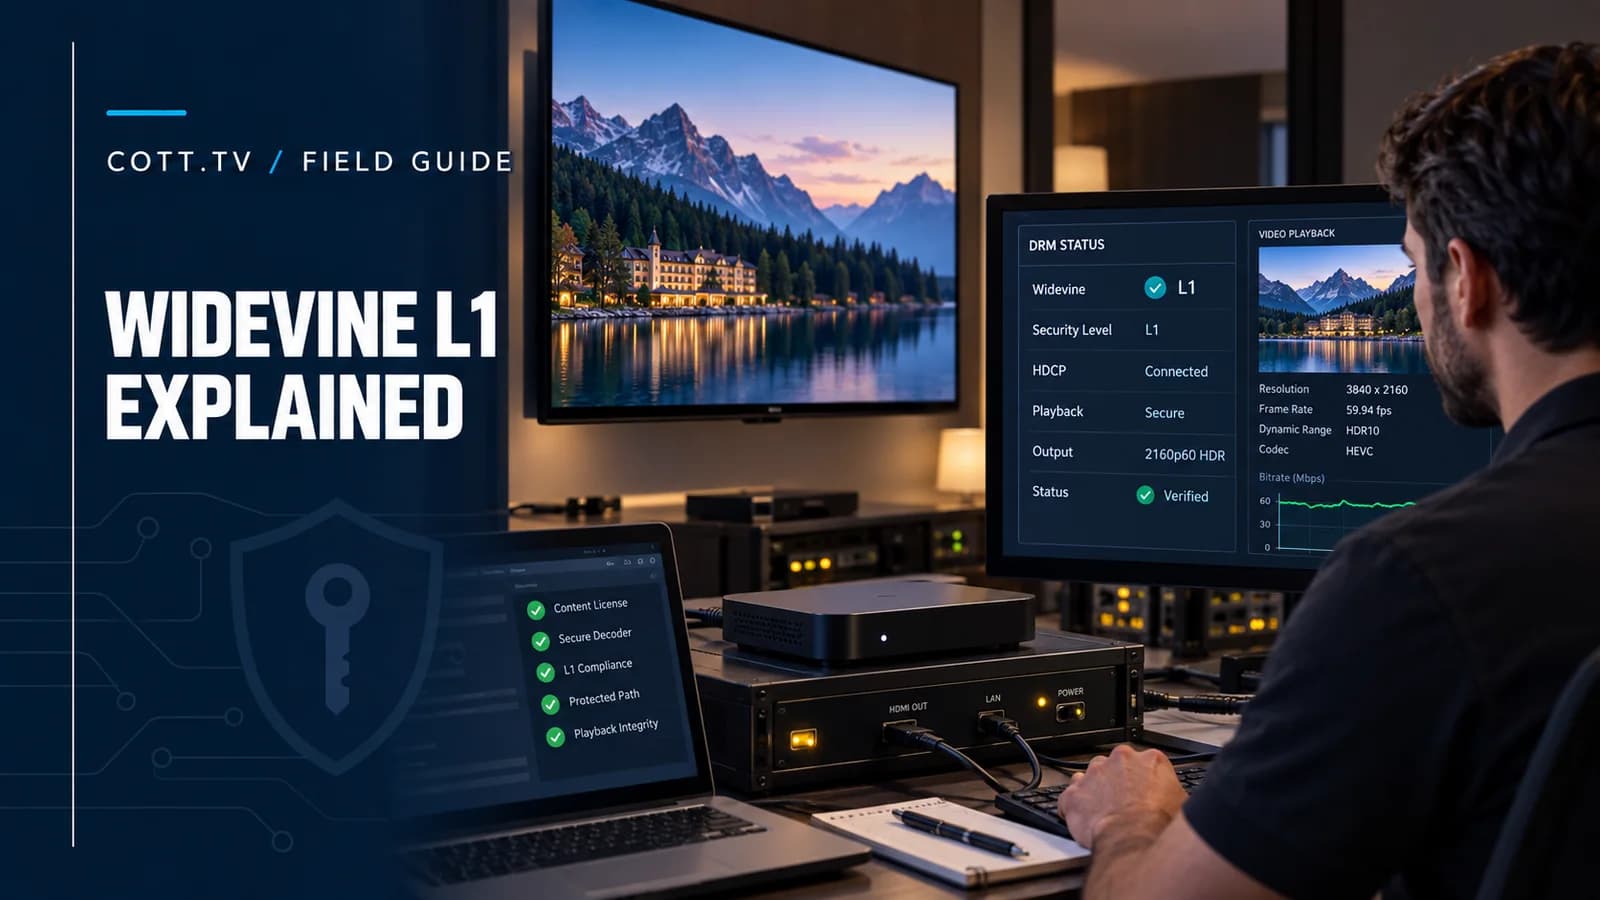
Quick Summary
Verify the reported Widevine level, hardware secure path, HDCP, encryption scheme, manifest, licence proxy, player and content-provider policy together. Record real playback at the required resolution after cold boot, standby and network interruption. Widevine support is not t…
By the COTT.TV Hospitality Technology Research Desk | Researched September 2026
Widevine L1 is frequently treated as a badge: the device reports L1, so premium channels will work. In production, the result also depends on encryption scheme, licence policy, player, output protection, television handshake, provisioning and the rights granted by the content provider.
The hotel should promise encrypted content only after the exact stream has played on the exact endpoint and display profile under the intended commercial policy.
What Widevine does
Widevine is Google's content-protection system for premium media. It works with common web and media standards including Encrypted Media Extensions and Common Encryption. Google lists Android, AOSP, Chromecast, common browsers and smart-TV platforms including Tizen and webOS among supported platform categories.
At a high level:
1. content is packaged and encrypted; 2. the player loads a DASH or HLS presentation; 3. the client creates a licence challenge; 4. the operator's licence proxy validates entitlement and policy; 5. the Widevine service returns a device-specific licence; 6. the client decrypts and renders through the permitted path.
The licence proxy is important. Google states that the client does not communicate directly with the Widevine licence service; the partner-operated proxy validates the request and applies business rules.
Security levels in practical terms
L1: cryptographic processing and protected media handling occur inside a trusted execution environment. This is commonly required for high-definition or ultra-high-definition premium content.
L3: decryption relies more heavily on the normal software environment. Many services restrict resolution or deny playback.
The device's diagnostic property is only one input. A poorly integrated firmware can report L1 while failing the content provider's robustness or output requirements.
Encryption schemes and compatibility
Google's Widevine documentation shows that platform support for Common Encryption schemes varies by generation. Modern Android TV versions and smart TVs commonly support cenc and cbcs, but older endpoints may be narrower.
Capture for each channel:
- 1container and streaming protocol;
- 2video and audio codecs;
- 3cenc or cbcs encryption;
- 4key rotation behaviour;
- 5manifest signalling and PSSH data;
- 6licence URL and authentication route;
- 7required output protection;
- 8offline or persistent-licence policy if relevant.
Do not change encryption mode across the contribution and distribution pipeline without retesting every endpoint profile.
L1 does not guarantee 4K
Resolution can be constrained by:
- 1content-provider licence policy;
- 2device security certification;
- 3HDCP level on the HDMI output;
- 4display EDID and handshake;
- 5codec profile and hardware decoder;
- 6application or browser limits;
- 7account or territory entitlement;
- 8network capacity.
The acceptance record should state the observed resolution and output-protection status, not simply "DRM passed."
Direct smart TV versus HDMI STB
On a direct smart-TV application, the platform controls the media pipeline and display together. On an STB, the protected path also crosses HDMI. That introduces HDCP negotiation and television compatibility.
Test the intended cable, port and power sequence. A stream that works after reconnecting HDMI manually may still fail after the room's nightly power cycle.
The licence-policy questions
Ask the content provider or DRM operator:
- 1which territories and properties are authorised;
- 2whether entitlement is per room, device, property or account;
- 3required security level and minimum HDCP;
- 4maximum resolution by device profile;
- 5concurrency and session limits;
- 6token and licence duration;
- 7whether device revocation is supported;
- 8log and reporting requirements;
- 9test and production credential separation;
- 10incident and key-rotation procedure.
Do not place production DRM credentials in a downloadable television package. The application should request short-lived authorisation through a controlled backend.
A real acceptance test
Use one clear channel and one encrypted channel with the same approximate video profile. This isolates DRM from basic decode and network issues.
For every endpoint profile:
1. confirm device time and trusted certificates; 2. record Widevine level and system identifier; 3. start the clear reference channel; 4. start the encrypted channel and capture licence result; 5. verify resolution, codec, audio and subtitles; 6. play for at least 30 minutes; 7. change channels repeatedly; 8. enter standby and resume; 9. cold boot and play again; 10. interrupt the network during playback; 11. restore the network and observe recovery; 12. revoke or expire the entitlement and confirm denial; 13. restore entitlement without reinstalling the application.
Capture player, application, firmware, television, STB, HDMI port and DRM policy versions. Video on the screen is necessary evidence, but support teams also need enough telemetry to understand future failures.
Diagnosing common failure layers
| Symptom | Likely investigation |
|---|---|
| Clear channel works, encrypted does not | Licence, DRM provisioning, entitlement or encryption profile |
| Audio plays, video is black | Secure decoder, HDCP, codec or display path |
| Works at 720p, fails at 1080p/4K | Robustness, HDCP or codec profile |
| Works once, fails after reboot | Device time, provisioning persistence or application startup |
| Licence returns 403 | Token, territory, room/device claim or proxy policy |
| Random failures at scale | Concurrency, proxy capacity, time sync or credential reuse |
Avoid putting raw keys, complete tokens or guest identifiers into general application logs.
DRM and stream authorisation are different layers
DRM protects the media keys and playback policy. CDN authorisation controls who can fetch manifests and segments. A robust service commonly needs both:
- 1short-lived signed access to the stream path;
- 2licence entitlement bound to an authorised room or device;
- 3origin access restricted to the CDN or gateway;
- 4key and signing-secret rotation;
- 5monitoring for abnormal reuse and geography.
One layer should not be treated as a substitute for the other.
COTT.TV verification model
COTT.TV records encrypted-channel playback as part of a device profile rather than assuming it from a specification sheet. The platform can authorise by property, territory, room and registered device while the DRM service enforces the content policy.
Read Protecting Hotel TV Streams for the surrounding distribution controls and the content licensing guide for the rights layer.
Sources and further reading
- 1Google: Widevine DRM overview
- 2Google: Widevine documentation
- 3Google Cast: receiver architecture
- 4AWS: restricting access to private content
DRM certification and content rights are separate. Final approval belongs to the relevant content owner, DRM provider and tested device profile.
Related Posts
Android TV Boxes for Hotels: Google TV, AOSP, Widevine L1 and Kiosk Control
2026-09-26
How to select a manageable hotel STB by separating consumer certification, DRM security, device-owner control, networking and lifecycle support.

Hotel TV Channel Lineup by Guest Mix: A Rights-Aware Planning Method
2026-09-11
A country, language and guest-segment method for selecting hotel channels without buying a large package that nobody watches.
Multi-Property Hotel TV Management: Central Control Without Losing Local Relevance
2026-08-17
Hotel groups need one operating model for brand standards, rights, devices and analytics, while each property retains control of local services. Here is a practical governance design.